By Air Marshal Anil Khosla
Cybersecurity has become essential to modern life as individuals, businesses, governments, and institutions increasingly depend on digital technologies. A key part of cybersecurity education is the human element. Technical security controls alone cannot eliminate cyber risk. Weak passwords, phishing, social engineering, unsafe browsing practices, poor access management, and inadequate awareness can all contribute to security incidents. A broad treatment of cybersecurity can help readers appreciate the relationship between technology, people, processes, and organisational policies.
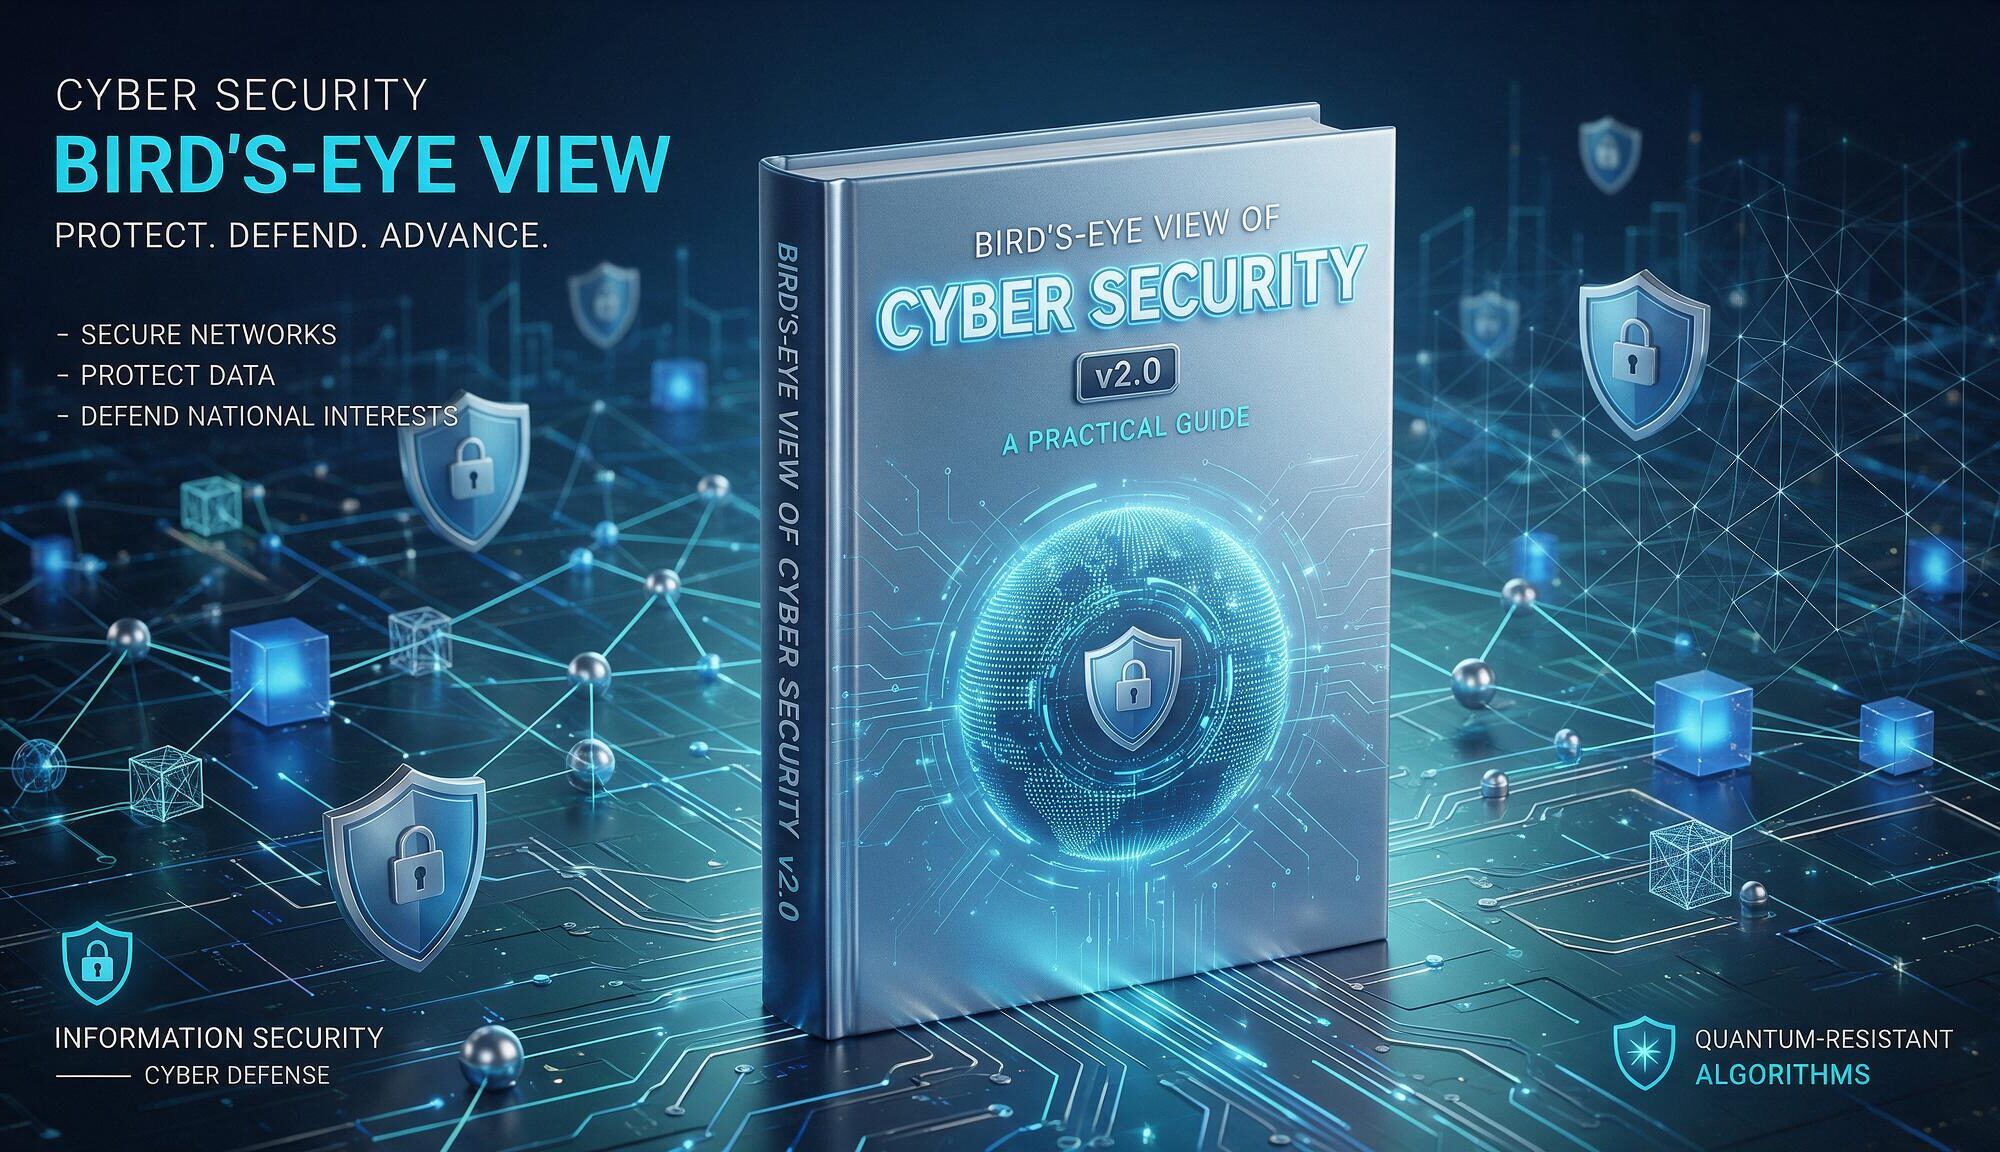
The book “Bird’s-Eye View of Cyber Security v2.0,” written by Biswajit Sahu, addresses this important topic by offering a broad, accessible account of cybersecurity. The title suggests the author aims to offer readers a comprehensive survey of the cybersecurity field rather than focus on a single technical aspect.
Biswajit Sahu is a Sr. Cybersecurity Consultant at Starlight Data Solutions (Bengaluru), with prior roles as a security engineer, presales engineer, and security analyst in Indian cybersecurity firms. The 134-page book (V2.0 edition, published March 2025, with paperback editions appearing in 2026) reflects his half-decade-plus industry experience and his work related to educating the cybersecurity community.
The book bridges the gap between foundational security concepts and the rapidly evolving technological frontiers reshaping domain defence. It is a concise, high-level map of the digital security landscape. The book systematically covers basic cyber hygiene, attack surface mapping, network security fundamentals, and Security Operations Centre (SOC) dynamics.
The 2.0 version goes beyond conventional IT security to include key operational areas such as Industry 4.0/OT systems, the security of critical national infrastructure, and the integration of autonomous or AI-powered threat detection. Because Sahu focuses on this subject, the text stresses the need for organisations to prepare for the coming post-quantum cryptography (PQC) era, explaining that they must adapt before existing encryption standards become vulnerable to quantum attacks.
True to its title, the text offers a thorough macro-level survey without getting into detailed code or vendor-specific settings. It draws on practical experience in real-world situations across critical infrastructure, defence and intelligence sectors, and law enforcement systems. A major advantage of a wide-ranging cybersecurity reference is that it helps readers understand the overall security ecosystem. The book’s concise structure makes it easy for decision-makers, cross-domain managers, and technical generalists who need a quick introduction to current cyber resilience requirements.
The main potential limitation of a high-level cybersecurity book is that breadth can sometimes come at the expense of technical depth. Readers with substantial experience in penetration testing, digital forensics, security engineering, malware analysis, or incident response may need more specialised resources for practical and advanced study. Thus, the book is particularly valuable as an overview and foundation, while specialised texts and hands-on laboratories remain important for developing advanced skills.
The topic is particularly relevant because cyber threats keep evolving as technology advances. Nowadays, organisations place greater trust in cloud services, connected devices, digital payments, remote working arrangements, and online platforms. As a result, cybersecurity needs to include not only technological protections but also user awareness. An effective introductory book on this subject should prompt readers to view security as an ongoing process which involves prevention, detection, response, and recovery.
Bird’s-Eye View of Cyber Security v2.0 can be viewed as a work aimed at developing a wider understanding of cybersecurity and its importance in the digital era. Its broad perspective is potentially useful for readers who want to understand how different aspects of cyber protection fit together. For students and newcomers to cybersecurity, such an approach can provide a foundation for further exploration of specialised areas. The book is a practical, quick-read executive briefing. It is particularly well-suited for military/defence leaders transitioning into multi-domain digital security, corporate executives seeking high-level risk literacy, or practitioners needing a broad framework to align emerging tech with threat readiness.
Please Add Value to the write-up with your views on the subject.
For regular updates, please register your email here:-
References and credits
To all the online sites and channels.
Pics Courtesy: Internet
Disclaimer:
The information and data in this blog are for educational & non-commercial purposes only and have been carefully adapted, excerpted, or edited from reliable and accurate sources. All copyrighted material belongs to the respective owners and is provided only for wider dissemination.