(Through AI Assurance, Model-Based Engineering, Certification and Tamper-Evident Technologies)
Trust in engineering is not simply a matter of reputation or confidence. In aerospace and defence, it means having evidence that a system will perform as intended, that its behaviour can be verified, that changes are controlled and that its integrity is maintained throughout its operational life.
Aviation has always operated on this principle. Every aircraft, flight-control system and avionics component must meet demanding safety and reliability requirements before entering service. However, as aerospace systems become increasingly software-intensive, connected and autonomous, demonstrating that level of confidence is becoming more challenging.
Artificial intelligence (AI), complex electronic hardware, digital engineering and global supply chains are changing how aerospace systems are designed, manufactured and maintained. Traditional verification and certification processes remain essential, but they must evolve to address technologies whose behaviour can be difficult to predict or explain.
The challenge is therefore not just to build systems that work, but to ensure that they remain understandable, verifiable, secure and reliable throughout their service life.
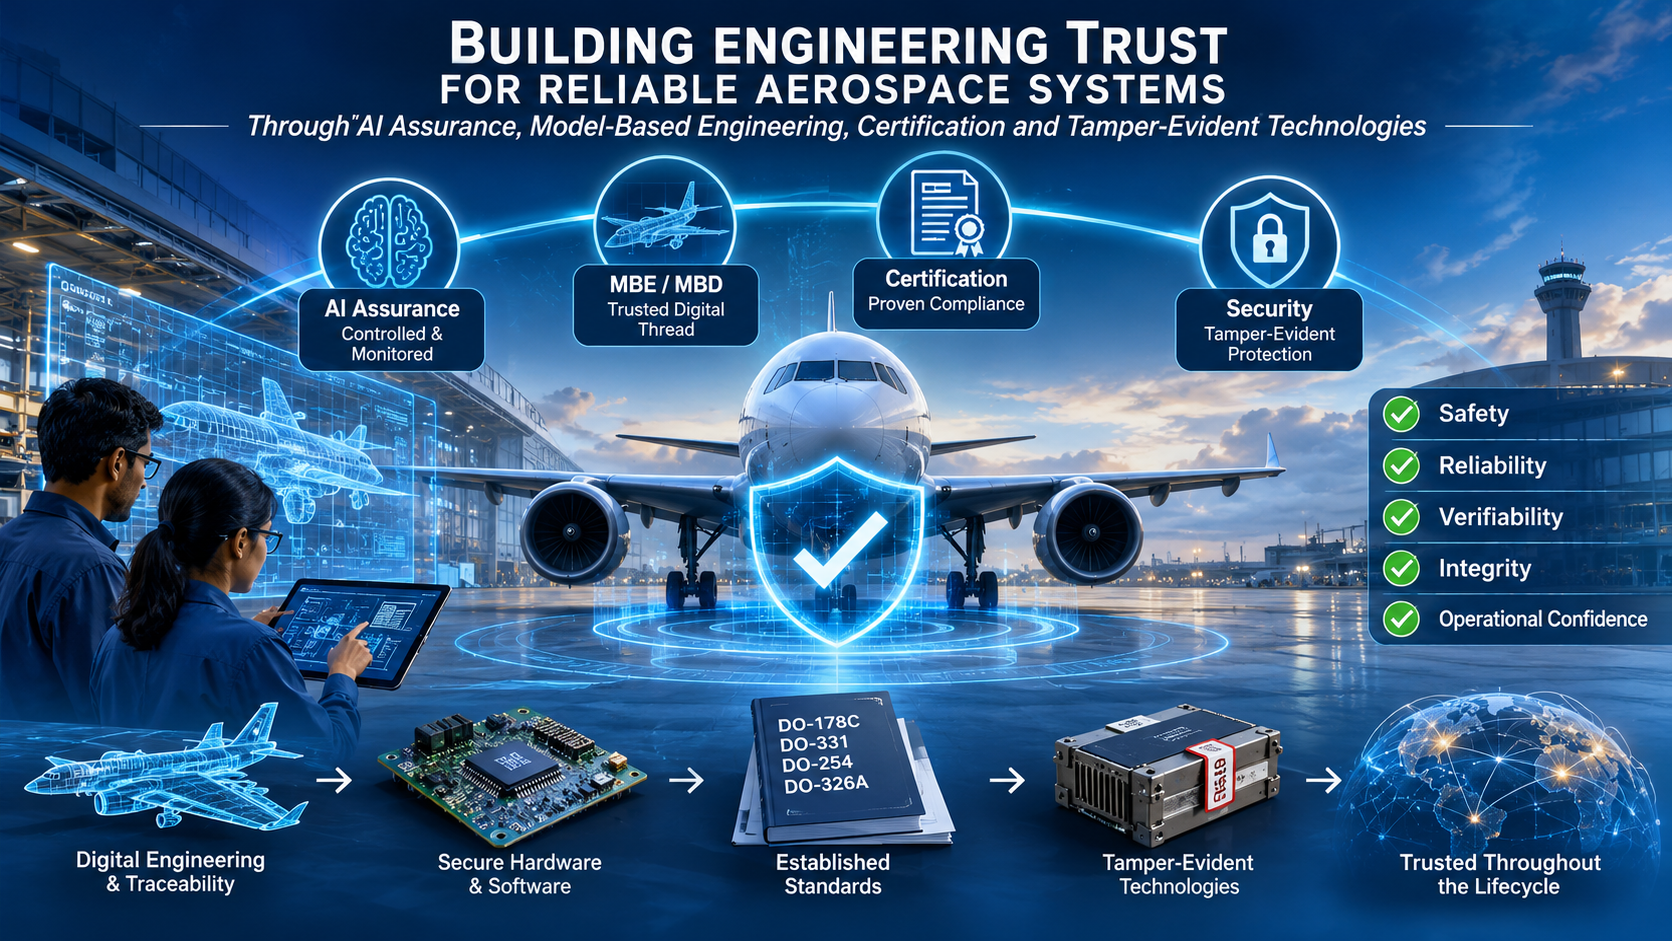
Four areas are particularly important: controlled integration of AI, Model-Based Engineering (MBE) and Model-Based Definition (MBD), aerospace design assurance standards, and technologies that protect systems against unauthorised modification.
Wrappers to Manage AI Trust Gap
AI is finding increasing application in aerospace, including predictive maintenance, automated inspection, navigation, surveillance, target recognition and autonomous mission management. Machine learning is particularly useful when systems need to interpret large volumes of complex data that conventional rule-based software may struggle to handle. However, introducing AI into safety-critical applications creates a significant assurance challenge.
Traditional software is developed against defined requirements. Its logic can be examined, functions traced to requirements and implementation verified through structured testing. Machine learning operates differently. A trained neural network derives its behaviour from training data and learned parameters rather than explicitly programmed rules. Although its performance can be tested across a range of scenarios, it is difficult to demonstrate that it will behave correctly under every possible operating condition. Its performance may also change when sensor quality, environmental conditions or input data differ from those encountered during training and validation. A high confidence score does not necessarily mean that an output is correct or safe.
One practical way of managing this uncertainty is through a controlled software architecture, often referred to as an AI wrapper or harness. The wrapper manages the AI model’s inputs and outputs, controls access to external data and functions, checks results and ensures that the model operates within defined limits. It can also incorporate independent monitoring, fault detection and fallback mechanisms.
The wrapper does not automatically make an AI model safe or certifiable. Its purpose is to place the model within an architecture where its limitations can be monitored and its influence controlled. This hybrid approach allows AI to perform tasks where machine learning offers clear advantages, while critical control functions and protective mechanisms remain within established engineering and verification processes. The wrapper, monitoring logic and interfaces must themselves be verified as part of the complete system.
Establishing a Reliable Digital Foundation with Model-Based Engineering/Definition (MBE/MBD)
Engineering trust also depends on consistency between what is specified, designed, manufactured and eventually maintained. In traditional engineering programmes, requirements, drawings, specifications and manufacturing information are often maintained in separate documents and systems. Although these remain useful, managing large volumes of information creates the risk of inconsistencies. A design change may be reflected in one document but missed in another, leaving manufacturing or maintenance teams working with outdated information.
Model-Based Engineering addresses this problem by using connected digital models throughout the product lifecycle. These models can represent requirements, system architecture, functional behaviour, physical design, manufacturing processes and verification activities. Linking them allows engineers to trace decisions and assess the impact of changes across the programme.
Model-Based Definition takes the approach further by making an annotated three-dimensional model the primary source of product definition. Instead of relying mainly on traditional two-dimensional drawings, the model contains Product Manufacturing Information (PMI), including dimensions, geometric dimensioning and tolerancing (GD&T), materials, surface finishes and manufacturing annotations. The objective is to establish an authoritative digital product definition that can be used by design, manufacturing, inspection and maintenance teams.
A Model-Based Enterprise extends this principle across the organisation and its supply chain. For aerospace programmes, where aircraft and components may remain in service for several decades, this continuity is particularly valuable. It improves configuration control, reduces interpretation errors and helps ensure that suppliers and maintenance organisations work from the same approved technical information.
MBE and MBD can also strengthen certification activities. Requirements can be linked to design features, simulations, verification results and approved configurations. When a change is proposed, its impact on the design and associated certification evidence can be assessed more systematically.
Established Standards for Aerospace Design Assurance
Aerospace is an industry in which reliability must be demonstrated through objective evidence rather than assumed. Certification authorities expect organisations to show that systems have been developed, verified and controlled in accordance with recognised safety and security requirements. Several standards form the basis of this approach.
DO-178C: Airborne Software Assurance.DO-178C, Software Considerations in Airborne Systems and Equipment Certification, is the principal industry standard for demonstrating the assurance of airborne software (its European equivalent is ED-12C). It defines objectives covering planning, software development, verification, configuration management, quality assurance and certification liaison. The level of rigour depends on the software’s contribution to aircraft safety. Design Assurance Levels range from Level A, associated with catastrophic failure conditions, to Level E, where software failure has no effect on aircraft safety. DO-178C is therefore much more than a coding standard. It establishes a disciplined process for demonstrating that airborne software meets its intended requirements and does not contain unintended functionality.
DO-331: Model-Based Development and Verification. DO-331 supplements DO-178C by providing guidance for model-based development and verification. Engineering tools are widely used to model system behaviour, simulate designs and, in some cases, generate software code. DO-331 recognises that models may form an important part of the development process and that verification must address the models themselves, their relationship with requirements, model coverage and generated software. This is particularly relevant to flight-control systems, guidance functions and other applications where simulation and executable models help engineers identify design problems before implementation.
DO-254: Airborne Electronic Hardware Assurance. Modern avionics rely on complex electronic hardware and programmable devices. DO-254, Design Assurance Guidance for Airborne Electronic Hardware, provides a framework for demonstrating the assurance of such hardware. Its processes cover planning, requirements capture, design, implementation, verification, configuration management and process assurance. The objective is to establish that electronic hardware performs its intended functions and that sufficient evidence exists to support its use in an aircraft. The FAA’s AC 20-152A recognises DO-254/ED-80 as an acceptable means of compliance for applicable airborne electronic hardware and provides additional guidance on areas such as custom devices, commercial off-the-shelf components and intellectual property. This is particularly important as avionics hardware becomes more sophisticated. A validated software algorithm cannot provide overall system assurance if the processing hardware, memory, interfaces and supporting electronics have not also been adequately verified.
DO-326A: Airworthiness Security. As aircraft become more connected to onboard networks, ground systems, maintenance equipment and external communication links, cybersecurity becomes an important part of airworthiness. DO-326A, Airworthiness Security Process Specification, together with its European counterpart ED-202A, addresses security threats that could affect aircraft safety. It provides a structured approach to identifying threats, assessing their potential impact and defining suitable security measures. These include access controls, network segregation, secure software updates, vulnerability management and protection against unauthorised modification.
Security must be considered during the design of the system rather than as an afterthought added on during development. In the case of connected aircraft and autonomous platforms, getting it right at the design stage is the only way to avoid the very real risk of a vulnerability undermining the safety of the system. The standards together provide a set of recognised processes for the assurance of software, model-based development, hardware and security. They don’t eliminate engineering risk, they just help the organisation to manage it and to demonstrate that it has done so via documented evidence.
Maintaining Integrity Through Tamper-Evident Technologies
Aerospace components pass through manufacturers, suppliers, maintenance organisations and operational units. During this process, hardware, firmware, software and configuration data may be exposed to accidental damage, unauthorised access or deliberate interference. Tamper-evident technologies help detect or record unauthorised physical and digital changes. Physical measures include numbered security seals, tamper-indicating labels, specialised coatings and markings that reveal whether an enclosure or component has been opened or altered. More advanced approaches use embedded sensing meshes, conductive circuits and intrusion-detection mechanisms.
Digital protection is just as important. Secure boot ensures that the device is booting from authorised software. Cryptographic signatures are used to authenticate firmware and software updates. Hardware roots of trust provide a secure base from which to do identity and integrity checks, with cryptographic hashes and signed audit records being used to detect changes to the configuration and data. All of this is particularly pertinent to AI enabled systems. An ML model which has been extensively validated is not going to be considered trustworthy if its parameters or software package are subsequently changed without authorisation.
In defence applications, anti-tamper technologies may also protect sensitive designs and critical programme technologies through secure key storage, tamper-sensing enclosures and controlled access to protected information. Such measures must be designed carefully. For example, automatically shutting down a system or erasing data following a detected intrusion must not introduce additional safety risks.
Tamper-evidence provides protection in conjunction with certification. Certification proves that the configuration in question satisfies its requirements. Integrity protection is what enables you to establish that the configuration has not been altered at a later date without detection.
Combining All the Elements
The real value of these disciplines comes from using them together rather than treating them as separate engineering initiatives. MBE and MBD provide a consistent digital definition of the system and establish traceability between requirements, design, manufacturing and verification.DO-178C, DO-331 and DO-254 provide established assurance processes for software, model-based development and complex electronic hardware. DO-326A addresses security risks that could affect airworthiness. AI wrappers, deterministic supervisory functions, runtime monitoring and fault-management mechanisms help control system behaviour during operation. Secure boot, cryptographic protection and tamper-evident technologies help preserve the integrity of the approved configuration. Each layer addresses a different source of risk. None is sufficient on its own.
Implications for India’s Aerospace and Defence Industry
For India’s aerospace and defence sector, engineering trust is becoming increasingly important as the country develops indigenous aircraft, UAVs, advanced avionics, space systems and autonomous platforms. Developing the technology is only part of the challenge. Indian organisations must also demonstrate that these systems are safe, secure, maintainable and suitable for operational use.
Wider adoption of MBE and MBD can improve engineering consistency, supplier integration and lifecycle data management. Building expertise in DO-178C, DO-331 and DO-254 will strengthen the ability of Indian organisations to develop and certify safety-critical avionics and electronic systems. Similarly, incorporating DO-326A principles and appropriate security controls into system architectures will help protect connected platforms against cyber threats and unauthorised modification. AI offers significant opportunities in perception, inspection, predictive maintenance and decision support. However, operational deployment must be supported by disciplined data management, model validation, uncertainty assessment and independent safety controls.
A hybrid architecture is a sensible way forward. There is also an important question of technological sovereignty. Dependence on externally developed black-box models, proprietary tools and components with limited technical transparency can create difficulties in assurance, maintenance and long-term support.
India therefore needs to build domestic capability in model validation, certification, secure hardware, digital engineering and mission software. The objective should not be to move away from international standards, but to develop the expertise needed to meet them while retaining control over critical technologies, engineering data and mission-specific software. This will strengthen operational capability and improve the international credibility of Indian aerospace products.
Concluding Thoughts
As aerospace systems become more intelligent, connected and autonomous, demonstrating their reliability will require greater engineering discipline.
AI offers capabilities that conventional software cannot always provide, but its use must be supported by appropriate controls and independent verification. MBE and MBD improve the consistency and traceability of engineering information. Aerospace standards provide established methods for demonstrating software, hardware and security assurance, while tamper-evident technologies help maintain system integrity throughout its service life. These disciplines are intimately linked. Digital models are of no use unless their information is properly governed. Certification is of any value at all if the approved configuration is maintained. AI can only be trusted in safety-critical applications if you understand its limitations and its failure modes.
Ultimately, engineering trust is not about claiming that a system is reliable, intelligent or secure. It is about demonstrating how it works, proving that it meets its requirements, controlling how it changes and ensuring that its integrity is maintained in service. That principle has guided aviation for decades and will remain just as important in future.
Please Add Value to the write-up with your views on the subject.
For regular updates, please register your email here:-
References and credits
To all the online sites and channels.
Pics Courtesy: Internet
Disclaimer:
Information and data included in the blog are for educational & non-commercial purposes only and have been carefully adapted, excerpted, or edited from reliable and accurate sources. All copyrighted material belongs to the respective owners and is provided only for wider dissemination.
References: –
- National Institute of Standards and Technology. (2023). Artificial intelligence risk management framework (AI RMF 1.0) (NIST AI 100-1). U.S. Department of Commerce. https://doi.org/10.6028/NIST.AI.100-1
- Federal Aviation Administration. (n.d.). Technical discipline: Artificial intelligence – Machine learning. https://www.faa.gov/aircraft/air_cert/step/disciplines/artificial_intelligence
- National Institute of Standards and Technology. (2024). Artificial intelligence risk management framework: Generative artificial intelligence profile (NIST AI 600-1). U.S. Department of Commerce. https://doi.org/10.6028/NIST.AI.600-1
- European Union Aviation Safety Agency. (2024). Artificial intelligence concept paper: Issue 2. EASA.
- European Union Aviation Safety Agency. (2020). Concepts of design assurance for neural networks (CoDANN). EASA.
- International Organization for Standardization. (2023). Systems and software engineering—System life cycle processes (ISO/IEC/IEEE Standard No. 15288:2023). ISO.
- International Organization for Standardization. (2025). Industrial automation systems and integration—Product data representation and exchange—Part 242: Application protocol: Managed model-based 3D engineering (ISO Standard No. 10303-242:2025). ISO. https://www.iso.org/standard/84300.html
- American Society of Mechanical Engineers. (2026). Digital product definition data practices (ASME Standard No. Y14.41-2026). ASME.
- International Organization for Standardization. (2019). Industrial automation systems and integration—Product data representation and exchange—Part 239: Application protocol: Product life cycle support (ISO Standard No. 10303-239:2019). ISO.
- International Council on Systems Engineering. (2023). Systems engineering handbook: A guide for system life cycle processes and activities (5th ed.). Wiley.
- RTCA, Inc. (2011). Software considerations in airborne systems and equipment certification (RTCA DO-178C). RTCA.
- RTCA, Inc. (2011). Model-based development and verification supplement to DO-178C and DO-278A (RTCA DO-331). RTCA.
- RTCA, Inc. (2000). Design assurance guidance for airborne electronic hardware (RTCA DO-254). RTCA.
- RTCA, Inc. (2014). Airworthiness security process specification (RTCA DO-326A). RTCA.
- RTCA, Inc. (2018). Airworthiness security methods and considerations (RTCA DO-356A). RTCA.
- Federal Aviation Administration. (2017). Airborne software development assurance using EUROCAE ED-12( ) and RTCA DO-178( ) (Advisory Circular No. AC 20-115D). U.S. Department of Transportation. https://www.faa.gov/regulations_policies/advisory_circulars/index.cfm/go/document.information/documentID/1032046
- Federal Aviation Administration. (2022). Development assurance for airborne electronic hardware (Advisory Circular No. AC 20-152A). U.S. Department of Transportation. https://www.faa.gov/regulations_policies/advisory_circulars/index.cfm/go/document.information/documentID/1041323
- Federal Aviation Administration. (2011). Development of aircraft and systems (Advisory Circular No. AC 20-174). U.S. Department of Transportation.